
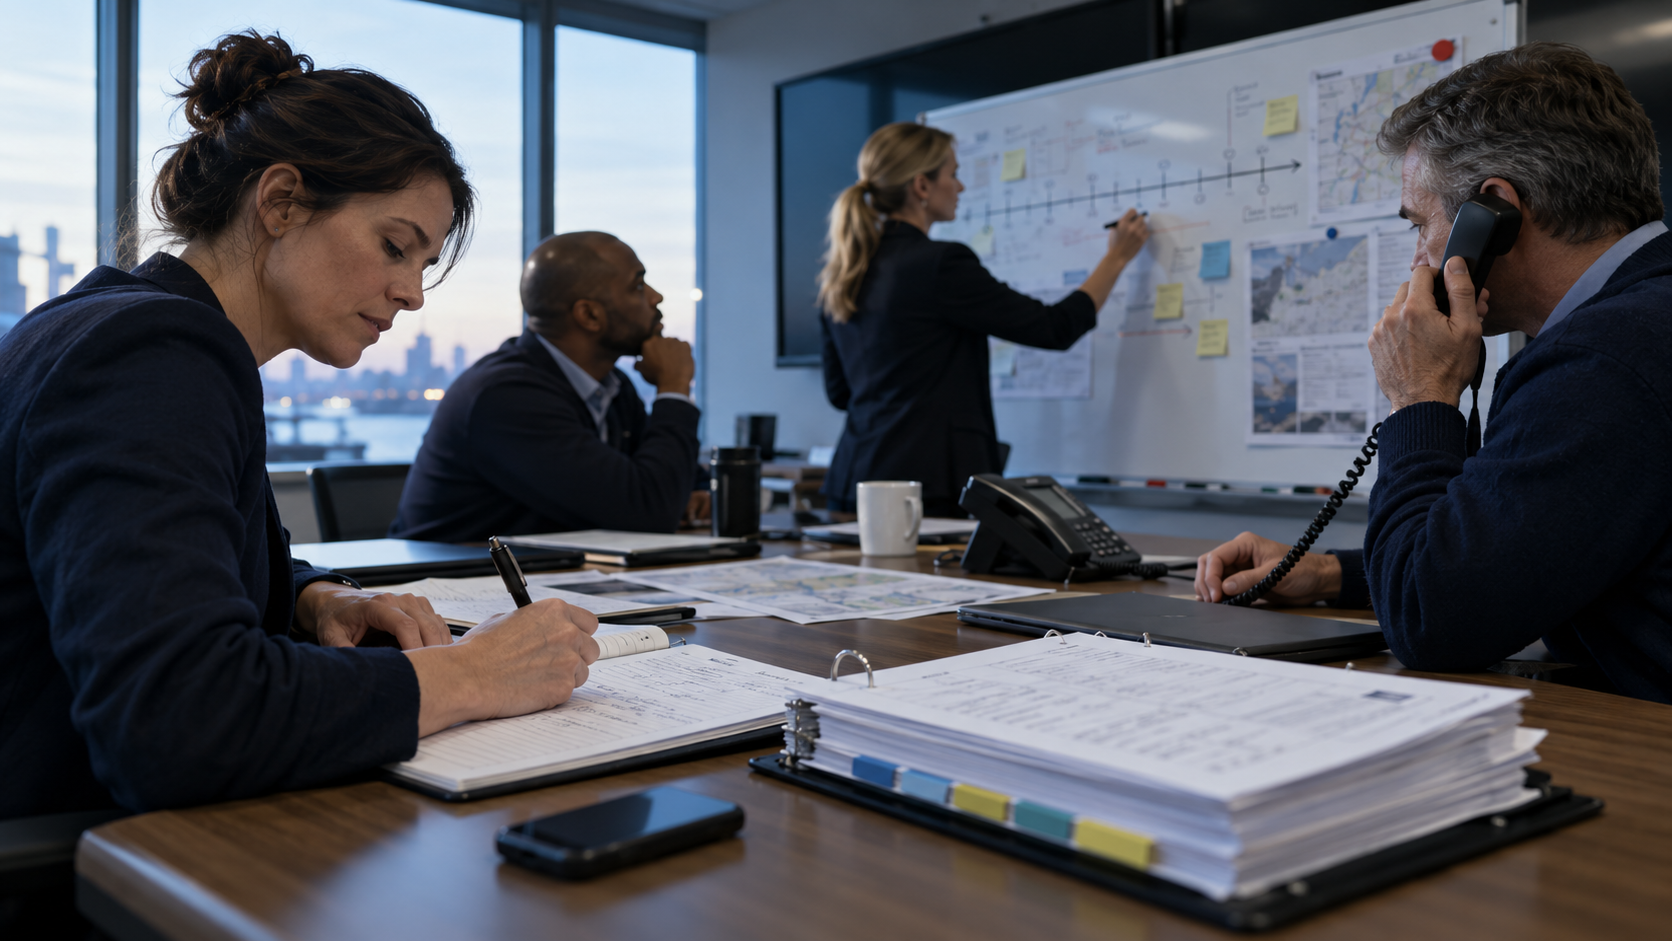
It is 7 a.m. Email is down, the crisis contact directory sits on an unreachable server, and the business continuity plan is stored… on the intranet. This is the paradox of many crisis arrangements: they depend on the very information system that has just failed.
This article sets out a method and a checklist to keep a crisis management team operational without its usual tools. Facts and recommendations drawn from public sources are identified as such; the method is a proposal from Exerce-Ease, to be adapted to your organisation.
What the references say
Sourced facts (see the list of sources at the end of the article):
- ANSSI, the French National Cybersecurity Agency, characterises a cyber-originated crisis by four features: a threat to the organisation’s priority objectives, the speed of the impacts, the technical complexity of the subject, and the evolving nature of the event, since attackers may react to the actions taken by the targeted organisation.
- Among its preparedness recommendations, ANSSI calls for a business continuity plan (BCP) that is resilient to cyberattacks and a disaster recovery plan (DRP), and for incident response capabilities to be prepared, including for the loss of the usual IT and communication resources.
- ANSSI also points out that exiting a crisis can take a long time: technical response, forensic investigation and system restoration can take several months.
- ISO 22301:2019 sets out the requirements for a business continuity management system, in particular to continue delivering products and services at an acceptable, predefined level during a disruption.
The practical consequence: the question is not only “how do we fix the IT system?”, but “how do we make decisions, communicate and keep essential activities running for days, or even weeks, without it?”.
A six-step method
1. Switch to degraded mode
Decide in advance who can declare the switch to degraded mode and on what criteria. Plan a physical assembly point and a way to convene the team that does not depend on the IT system: a telephone call tree, a conference bridge number, a printed list.
2. Communicate outside the information system
Treat email and internal collaboration tools as unavailable or potentially compromised. Activate backup channels that have been prepared and tested: phones and lines independent of the corporate network, a printed contact list, and simple rules on what may or may not be shared through these channels.
3. Run the crisis on paper
Open a time-stamped crisis log immediately (who, what, when, decision taken). Display a situation board: established facts, assumptions, decisions, actions in progress, next update. This record becomes the memory of the crisis and the basis for the lessons-learned review.
4. Protect essential activities
Go back to the list of priority activities identified in your business impact analysis (BIA). For each one: what is the maximum tolerable period of disruption, is there a manual workaround, and who triggers it? Anything not prepared before the crisis will be very hard to improvise during it.
5. Align decision-making and technical response
ANSSI recommends aligning crisis steering, on the business side, with incident response, on the technical side. Appoint a single point of contact between the decision-making team and the technical team, with synchronisation meetings at fixed times. The crisis team sets business priorities; the technical team reports on what is possible and when.
6. Sustain the effort over time
A long crisis wears teams out. Organise shift rotations, appoint deputies for every key role and set the meeting rhythm from day one. Plan internal communication too: staff deprived of their tools need clear and regular instructions.
Operational checklist
Before the crisis
- An offline crisis kit exists: printed crisis directory, quick-reaction sheets, printed business continuity plan, contact details of key suppliers and partners.
- Backup communication channels are identified, distributed and tested.
- The list of essential activities and their manual workarounds is up to date.
- Each crisis team role (lead, crisis secretariat, technical liaison, communication) has a named holder and a deputy.
- An incident response provider is identified and, where appropriate, under contract (ANSSI recommendation).
- The arrangements have been tested in an exercise simulating the loss of the IT system.
In the first hours
- Decision to switch to degraded mode taken and time-stamped.
- Crisis team convened in person or on a backup conference bridge.
- Crisis log and situation board opened.
- Single point of contact with the technical team appointed.
- First instructions sent to staff through a backup channel.
- Essential activities moved to manual workarounds where needed.
- Priority external stakeholders identified for communication.
Over time
- Situation updates at fixed times, with paper minutes.
- Shift rotations organised for the crisis team and technical teams.
- Decisions and actions tracked in the crisis log.
- Business units involved in the recovery plan and in the order in which services are restarted.
Exiting the crisis
- Crisis exit criteria defined and the decision formally recorded.
- Lessons-learned review organised on the basis of the crisis log.
- Prioritised improvement plan, with owners and deadlines.
Fictional example: a morning without IT
Fictional scenario, for teaching purposes. An 80-employee SME discovers at opening time that its workstations and servers are displaying a ransom demand. The CEO declares degraded mode and convenes the crisis team using the telephone call tree. The office manager opens the crisis log in a notebook. The IT manager becomes the single point of contact with the incident response provider. Urgent orders are processed using the paper order forms provided for in the BCP. At 10 a.m., a first message is sent to staff by SMS from backup phones: do not switch on workstations, wait for instructions from your manager.
This sequence only works if every element (call tree, paper forms, backup phones) has been prepared and tested beforehand.
Test your degraded mode before D-Day
ANSSI stresses the need to train in order to practise and improve, and in 2020 published, together with the Club de la continuité d’activité (French business continuity association), a guide dedicated to organising cyber crisis exercises.
An exercise focused on the loss of the IT system quickly reveals what no procedure review will show: the paper directory that is out of date, the conference bridge whose access code nobody knows, the manual workaround that only one person has mastered.
A useful action this week: ask your crisis team to find, without a computer or email, the phone numbers of three critical partners and the manual workaround for your most sensitive activity. Note how long it takes and what is missing.
To go further, Exerce-Ease lets you simulate an IT outage with realistic injects (SMS, phone calls, media requests, technical updates) and turn it into an actionable lessons-learned review.
Request a demo: https://www.exerce-ease.com/en/contact.php